

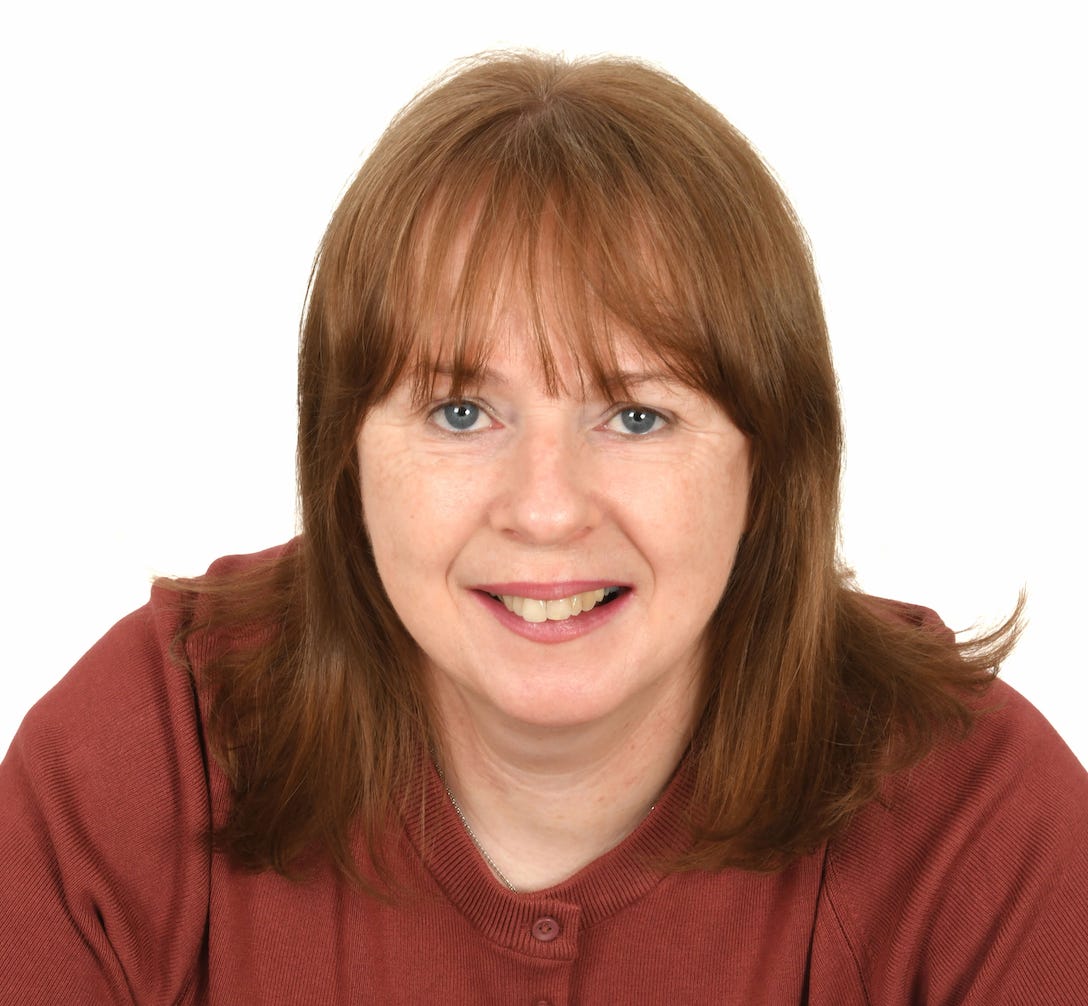
Geraldine Powderly is CISO & VP Technology at SkySpecs, a global renewable-energy technology company, where she leads technology, cybersecurity, and AI strategy across an internationally distributed business. Over 25 years, she has grown from software and quality engineering into global security and technology leadership, building programs from the ground up, scaling teams, governing multi-million-euro budgets, and delivering ISO 27001, SOC 2, and ISO 42001 assurance. She speaks regularly on AI adoption and governance, adaptive security leadership, zero trust, and cloud risk, including at ISC2 Security Congress and senior CIO/CISO forums.
Ask Geraldine how she explains technical risk to executives, and the answer involves a customer’s goldfish. Her answers for CISO Tips carry that same plain, practical style: a hard line on shared accounts, a habit of asking which hill the team is willing to die on, and a vendor test built around proving value in her environment rather than theirs. She also explains why alerts without owners should go and what replaced her recurring vulnerability remediation meetings.
Complete this sentence: “Before you buy any new security tool, first...”
Before you buy any new security tool, first consider the rollout plan and how your end user will experience this tool; understanding and buying in are critical parts to a security tool implementation.
What’s one rule you enforce on your team that other teams would find strict?
No shared accounts, ever!
What’s a number or ratio that guides how you allocate budget, headcount, or your own time?
In security the number of risks and gaps that need to be addressed can be overwhelming. Even after a risk assessment, you still end up with a large number of critical issues. I follow the rule of Security Risk vs. Business Risk, and also a question that I often ask myself and the team: “Which hill are we willing to die on?” That tends to get you to the answer pretty quickly!
What’s one line that works when asking the board or CFO for a budget?
This investment protects our ability to deliver on our business commitments.
What should a CISO cut from their program tomorrow with zero regret?
Alerts with no owners.
What’s your 60-second test for whether a vendor pitch is worth your time?
“How quickly we can prove the value of your solution in our environment, not yours.” This gives a quick understanding of the rollout complexity.
What’s one meeting, report, or process you eliminated, and what replaced it?
I replaced recurring meetings debating vulnerability remediation with risk-based prioritization, DevSecOps ownership and team resolution leaderboards. Less discussion, more accountability.
In the first 10 minutes of an incident, what’s the one action teams most often skip?
Agreeing on the actual facts of what has occurred and who should be involved in the incident at that time.
What’s one question every CISO should ask their team this week?
“Do we know where or how our data is leaking this week?”
What’s a phrase or framing you use to translate a technical risk for executives?
“Our customer has asked us to mind their goldfish, and it’s imperative that the goldfish does not die while we are responsible for it!”
What’s your best tip for surviving the CISO role in exactly five words?
Build trust. Make risk-based decisions.
More tips from the series:
CISO Tips: Curtis Blais on Treating Cyber Risk as Mission Risk
CISO Tips: Dean Navarro on Tying Every Security Dollar to Business Risk
CISO Tips: Jon Murphy on Finding the Signal and Ignoring the Noise
CISO Tips: Merlin Namuth on Earning Trust and Measuring Everything Against Risk
CISO Tips: Samuel Keter on Turning Security Controls Into Business Decisions