

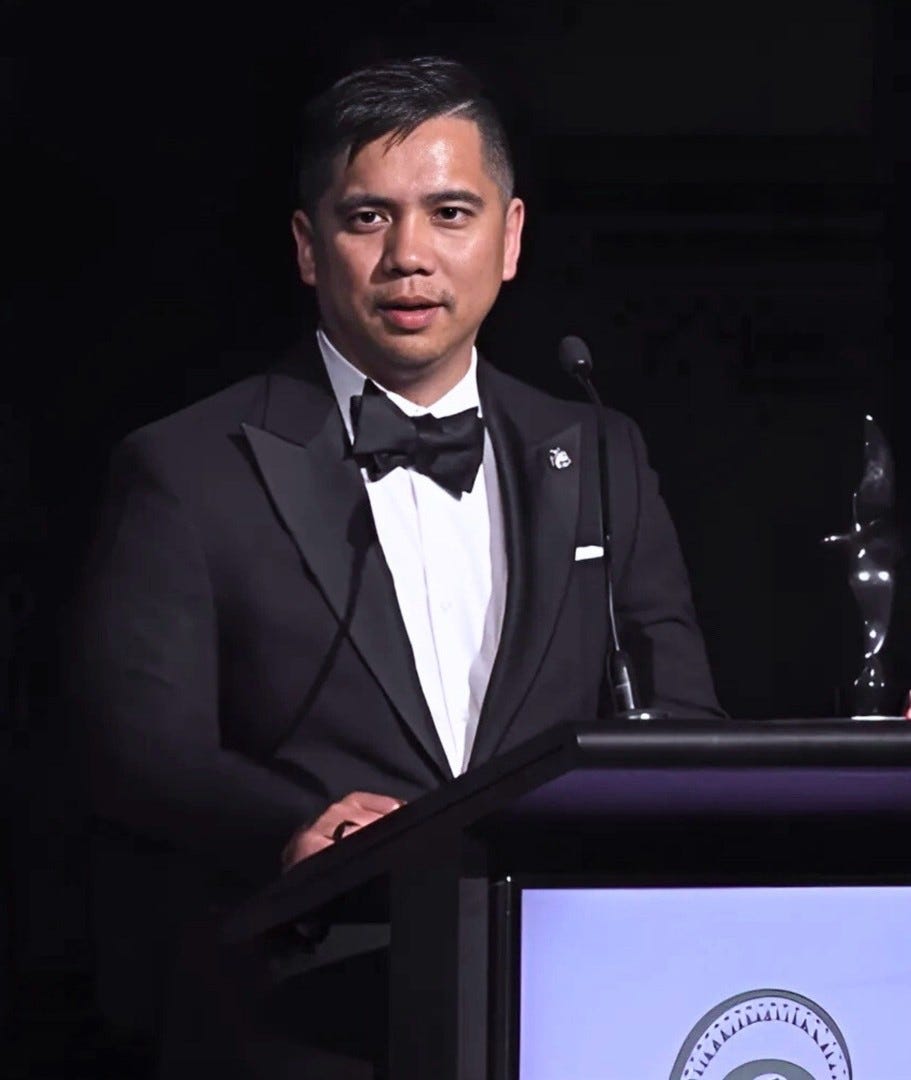
Dean Navarro is an information security and privacy leader who believes security is most effective when it enables the business rather than constrains it. Having led award-winning security teams, he is passionate about helping organisations move beyond compliance-driven security, improve risk visibility, and make better decisions through collaboration, trust, and shared ownership.
For Navarro, security earns its place when every investment, metric, and recommendation connects back to the business. His approach includes tracing all security spending to a risk, obligation, or strategic objective, cutting reporting that doesn’t drive decisions, and presenting a united position to the business once the team has debated internally. In this edition of CISO Tips, Navarro shares practical lessons on budget asks, vendor pitches, incident response, team alignment, and communicating risk to executives.
Complete this sentence: “Before you buy any new security tool, first...”
Before you buy any new security tool, first understand the requirement, the risk you’re mitigating, and whether your existing technology stack can already do the job.
What’s one rule you enforce on your team that other teams would find strict?
We must sing the same song when engaging with the business. Healthy debate happens within the team, but once we align on a position, we present a consistent message and recommendation.
What’s a number or ratio that guides how you allocate budget, headcount, or your own time?
100% of security investment should be traceable to a business risk, compliance obligation, or strategic objective. If it isn’t, I challenge why we’re spending the money.
What’s one line that works when asking the board or CFO for budget?
Here’s the risk, here’s the impact, here’s the treatment option, and here’s the risk we’ll continue to carry if we do nothing.
What should a CISO cut from their program tomorrow with zero regret?
Metrics and reporting that don’t drive a decision. If nobody changes their behaviour after seeing it, stop producing it.
What’s your 60-second test for whether a vendor pitch is worth your time?
If I haven’t identified a requirement, I’m probably not the right audience for the pitch.
What’s one meeting, report, or process you eliminated, and what replaced it?
I’ve worked to shift from static compliance to dynamic risk management. Meeting a requirement is important, but understanding, prioritising, and reducing risk is what creates value.
In the first 10 minutes of an incident, what’s the one action teams most often skip?
Making sure the right people are on the call. Too often, teams invite everyone and end up with a crowded bridge instead of a coordinated response.
What’s one question every CISO should ask their team this week?
How are we doing as a team, and what do we need to be successful?
What’s a phrase or framing you use to translate a technical risk for executives?
I don’t rely on a specific phrase. I focus on explaining the business impact and how the risk could affect our strategic objectives, rather than the technical details.
What’s your best tip for surviving the CISO role in exactly five words?
Listen. Understand. Prioritise. Deliver together.
More tips from the series:
CISO Tips: Jon Murphy on Finding the Signal and Ignoring the Noise
CISO Tips: Merlin Namuth on Earning Trust and Measuring Everything Against Risk
CISO Tips: Samuel Keter on Turning Security Controls Into Business Decisions
CISO Tips: Bryce Austin on Building a Security Program That’s “Secure Enough”
CISO Tips: Stefano Pasotti on Turning Cybersecurity Into Business Resilience