

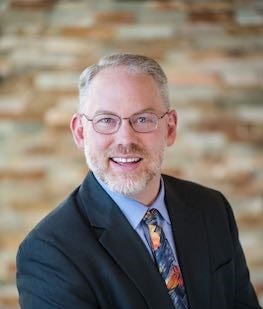
Merlin Namuth is the Chief Information Security Officer at the City and County of Denver, where he leads security for over 50 agencies and departments. His experience spans multiple industries and includes building security programs from the ground up, advancing mature programs, leading incident response, and handling compliance, architecture, and mergers and acquisitions. A regular conference speaker and security startup advisor, he is also an active writer and podcast guest in the security community.
For Namuth, security leadership comes down to risk and trust. His approach includes weighing every tool purchase and budget request against the risk it reduces, cutting work that doesn’t move the program forward, and building relationships across the organization before a crisis hits. In this edition of CISO Tips, Namuth shares practical lessons on budgeting, vendor evaluation, incident response, team culture, and translating technical risk for executives.
Complete this sentence: “Before you buy any new security tool, first...”
Before you buy any new security tool, first understand what risk it will address, how much it will reduce that risk, and if the cost justifies the impact it will have on risk.
What’s one rule you enforce on your team that other teams would find strict?
We are in a position of high trust in the organization, and it is very important for us to have high integrity, adhere to the policies and rules, and help everyone who comes to our team, whether or not their issue falls within something we support and can fix. Trust takes a lot of work to earn and can go away in an instant with a bad decision.
What’s a number or ratio that guides how you allocate budget, headcount, or your own time?
It is based on the severity of the risk and how reducing this risk will positively or negatively impact the business.
What’s one line that works when asking the board or CFO for a budget?
I explain the risk and how an increased budget will reduce that risk. Conversely, I share how no change in budget will keep the risk the same, and the potential costs to the business if it is exploited.
What should a CISO cut from their program tomorrow with zero regret?
Work the team is doing that doesn’t reduce risk or mature the security program.
What’s your 60-second test for whether a vendor pitch is worth your time?
If the solution solves a current challenge I have and fits in my current roadmap. When the vendor says they can have their solution running and providing value within 15 minutes, I tend to eliminate them from consideration.
What’s one meeting, report, or process you eliminated, and what replaced it?
I canceled weekly status meetings with my team because we had enough informal conversations for me to be informed. Too many meetings is malware.
In the first 10 minutes of an incident, what’s the one action teams most often skip?
Getting the right people involved, which should be outlined in the incident response plan.
What’s one question every CISO should ask their team this week?
I usually lead with “How are you?” I want my team to feel valued and appreciated, and to know that everything we do is part of the team. If one person on the team is struggling with something, it is the responsibility of the rest of the team to help out.
What’s a phrase or framing you use to translate a technical risk for executives?
In my current role as CISO for the City and County of Denver, I discuss how something can impact our public safety agencies and our residents.
What’s your best tip for surviving the CISO role in exactly five words?
Build relationships before crisis hits.
More tips from the series:
CISO Tips: Samuel Keter on Turning Security Controls Into Business Decisions
CISO Tips: Bryce Austin on Building a Security Program That’s “Secure Enough”
CISO Tips: Stefano Pasotti on Turning Cybersecurity Into Business Resilience
CISO Tips: Maurizio Imperadore on Resilience, Identity and Cutting Security Noise
CISO Tips: Jigar Shah on Buying Fewer Tools, Building More Trust