

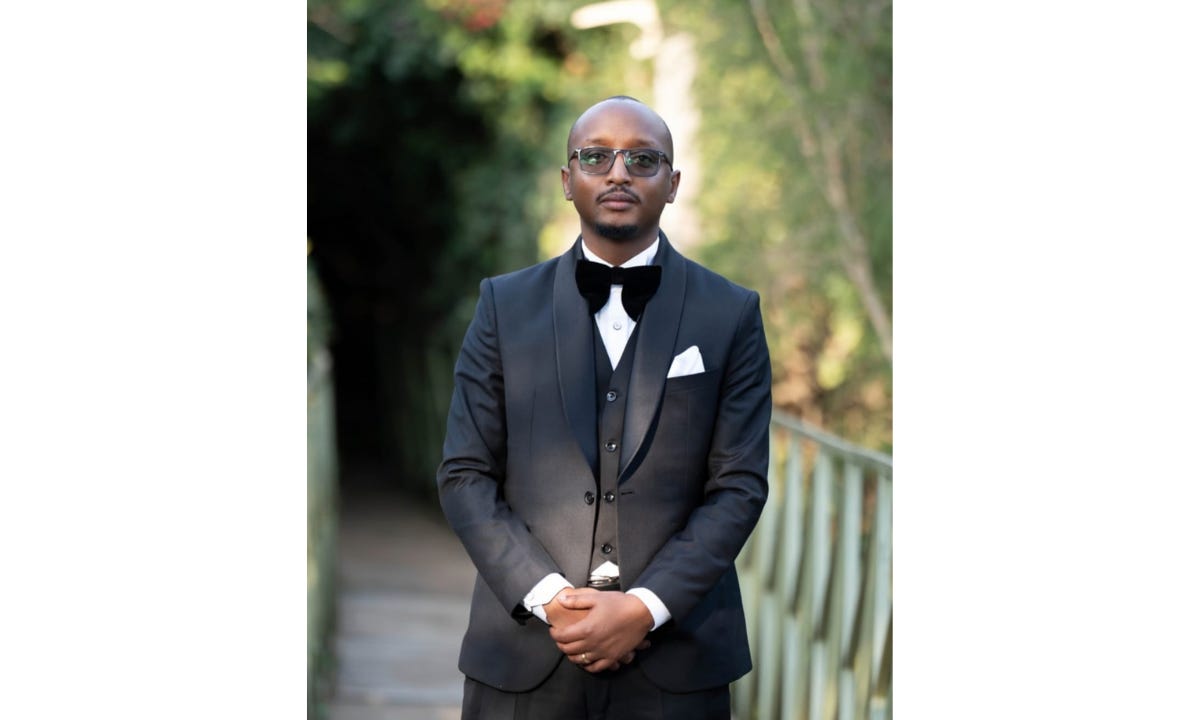
With more than a decade of experience across cloud security, audits, risk management and security governance, Samuel Keter has worked at the intersection of cybersecurity and business operations across banking, fintech and consulting organizations. He has led teams through ISO 27001, PCI DSS, SOC 2 and NIST programs, managed complex cloud and on-premises audits, and advised executive leadership on security risks and controls across multiple regions.
For Keter, effective security leadership is less about accumulating tools and metrics and more about building systems that reduce measurable risk. His approach includes testing what existing technology can already accomplish before buying new products, enforcing security gates in development pipelines, allocating resources according to risk, and translating technical exposure into numbers executives already understand. In this edition of CISO Tips, Keter shares practical lessons on budgeting, incident response, cloud identity, compliance evidence and making security decisions that hold up under scrutiny.
Complete this sentence: “Before you buy any new security tool, first...”
Before you buy any new security tool, first build the simple version with what you already own. We scripted a cloud misconfiguration audit across every project before looking at a posture product. The audit identified most of the issues that the demo had presented. The identified gaps formed the basis for the shortlist and our negotiating position.
What’s one rule you enforce on your team that other teams would find strict?
Nothing merges without a signed commit and a green security gate, and the gate is required verification, not advisory. It blocked a release in its first week, and the team fixed the finding rather than disabling the verification. That decision is the rule. Most teams have the same policy but a pipeline that doesn’t enforce it.
What’s a number or ratio that guides how you allocate budget, headcount, or your own time?
70, 20, 10. 70% of the budget and headcount is allocated to risk reduction, 20% to proof, and 10% to options. Workload identity to kill static keys retires a register item, so it comes from the 70. Compliance automation that collects control evidence on a schedule reduces no risk but makes SOC 2 and PCI DSS continuous, so it comes from the 20. A month for an engineer to build an alert triage agent might fail, so it comes from the 10. A second dashboard is not being developed because someone prefers the interface, so it remains on hold.
What’s one line that works when asking the board or CFO for a budget?
This expense is not security spending. It is the cost of keeping our license to process payments. Then I put the control cost next to the share of revenue running over card rails, and the conversation becomes about their exposure rather than my budget.
What should a CISO cut from their program tomorrow with zero regret?
Do not use any metric that counts items unless it influences a decision. We dropped total open vulnerabilities from the executive report and replaced them with exploitable findings on internet-facing assets and the median days to close. The total rose the next month because we found more. Nobody asked, because the numbers that mattered fell.
What should a CISO cut from their program tomorrow with zero regret?
I ask how the product authenticates to my cloud. A service account key with an owner role fails the test I hold my engineers to, and the meeting is over. Federated identity, scoped permissions, and an expiring token earn the next twenty minutes.
What’s one meeting, report, or process you eliminated, and what replaced it?
The weekly alert review involves five people reading raw findings displayed on a screen. A monitoring agent now ingests events from source control, applies a rule-based severity floor before the model sees them, and logs every decision to an audit table. It ran in shadow mode for weeks, with the team grading its calls before anything was routed based on its output. The audit table is now our evidence for the monitoring control.
In the first 10 minutes of an incident, what’s the one action teams most often skip?
Stopping the pipeline. In a package registry compromise this year, freezing CI and pinning the package took under ten minutes. Working out how it was poisoned took days. Teams do those in the wrong order, and every build in between pulls the compromised version again.
What’s one question every CISO should ask their team this week?
If an auditor asked for evidence of this control at nine tomorrow, what would we be able to provide? Ask about one control each week. The phrase “I would have to pull it together” indicates that while the control is legitimate, the supporting evidence is lacking, which is the basis for the next audit finding.
What’s a phrase or framing you use to translate a technical risk for executives?
Three numbers the board already tracks: customers exposed, money at risk, and hours until we would know. A permissive IAM binding means nothing to them. Every customer in the wallet database, the balance held there, and four days before detection fires gets a decision in the same meeting.
What’s your best tip for surviving the CISO role in exactly five words?
Trust nothing. Log everything. Sleep.
More tips from the series:
CISO Tips: Bryce Austin on Building a Security Program That’s “Secure Enough”
CISO Tips: Stefano Pasotti on Turning Cybersecurity Into Business Resilience
CISO Tips: Maurizio Imperadore on Resilience, Identity and Cutting Security Noise
CISO Tips: Jigar Shah on Buying Fewer Tools, Building More Trust
CISO Tips: Andy Curtis on Turning Cybersecurity Into Business Risk Decisions